Erebus forensically maps the technical infrastructure behind disinformation campaigns. From a flagged site to the actor network behind it, with every claim traceable to evidence.
For government agencies, defense organizations, election bodies, and CTI and platform integrity teams across Europe.
3influence operations unmasked in published joint investigations
98.5%identical page structure between "unrelated" news outlets
476byte-identical images recurring across 18 amplifier sites
3,278archived snapshots forensically analyzed in one investigation
45campaigns of fabricated stories attributed to one operation
The problem
Disinformation campaigns are typically detected at the narrative level. But the technical infrastructure behind them, such as domains, hosting, DNS patterns, and registration chains, often goes unexamined.
This leaves a blind spot between information operations and cyber threat intelligence. The actors running coordinated fake news sites frequently share infrastructure with entities involved in conventional cyber operations. Without forensic analysis of that infrastructure layer, the network stays a set of unconnected sites and the actor behind it stays unnamed.
With the Atlantic Council's DFRLab · March 31, 2026
A Polish-language "news outlet" that ran for five years. Our forensic analysis of 3,278 archived snapshots established it as a likely foreign influence operation and surfaced the operators behind it.
Russian-language fingerprints embedded throughout the site's HTML, invisible to readers, unambiguous in the forensics.
Fabricated editorial personas fronting the outlet, built on photos stolen from Russian social media accounts.
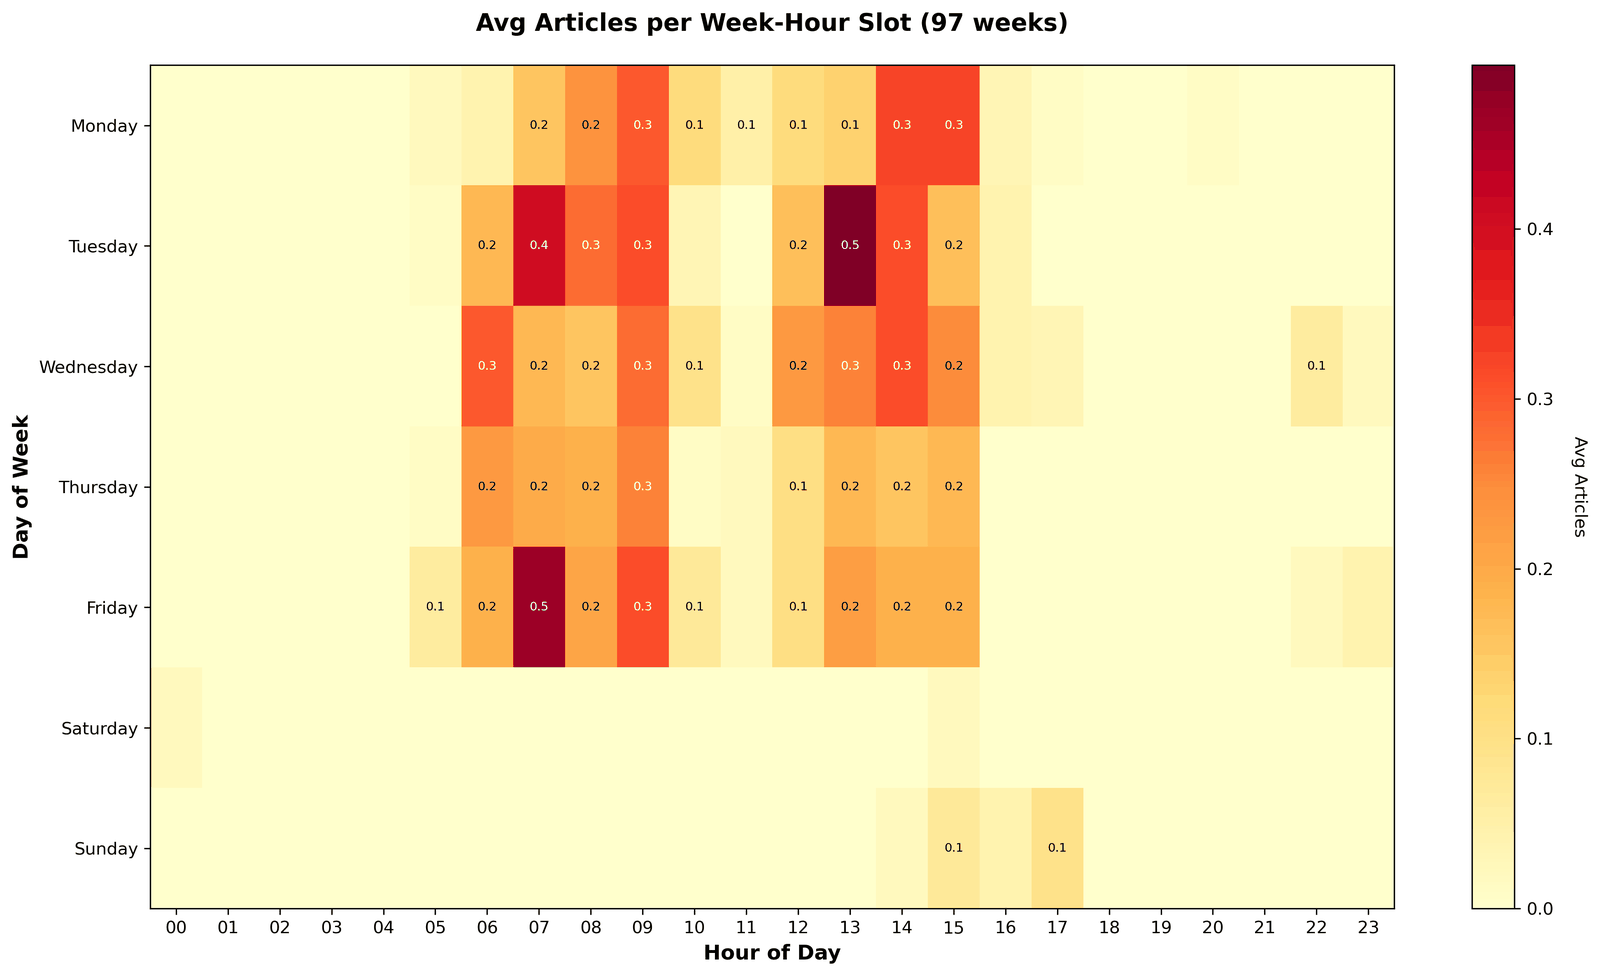
Publishing clustered within Minsk and Moscow business hours, not Warsaw's.
The site's most hostile sections went silent four days after Poland's October 2023 parliamentary elections.
With the Atlantic Council's DFRLab and CivilNet · July 29, 2026
A modern influence operation does not run one website; it runs a fleet. Ahead of Armenia's 2026 parliamentary elections, we took a network of sites posing as independent local outlets and showed they were built with shared tooling.
Three coordinated website clusters, all presenting as independent news outlets.
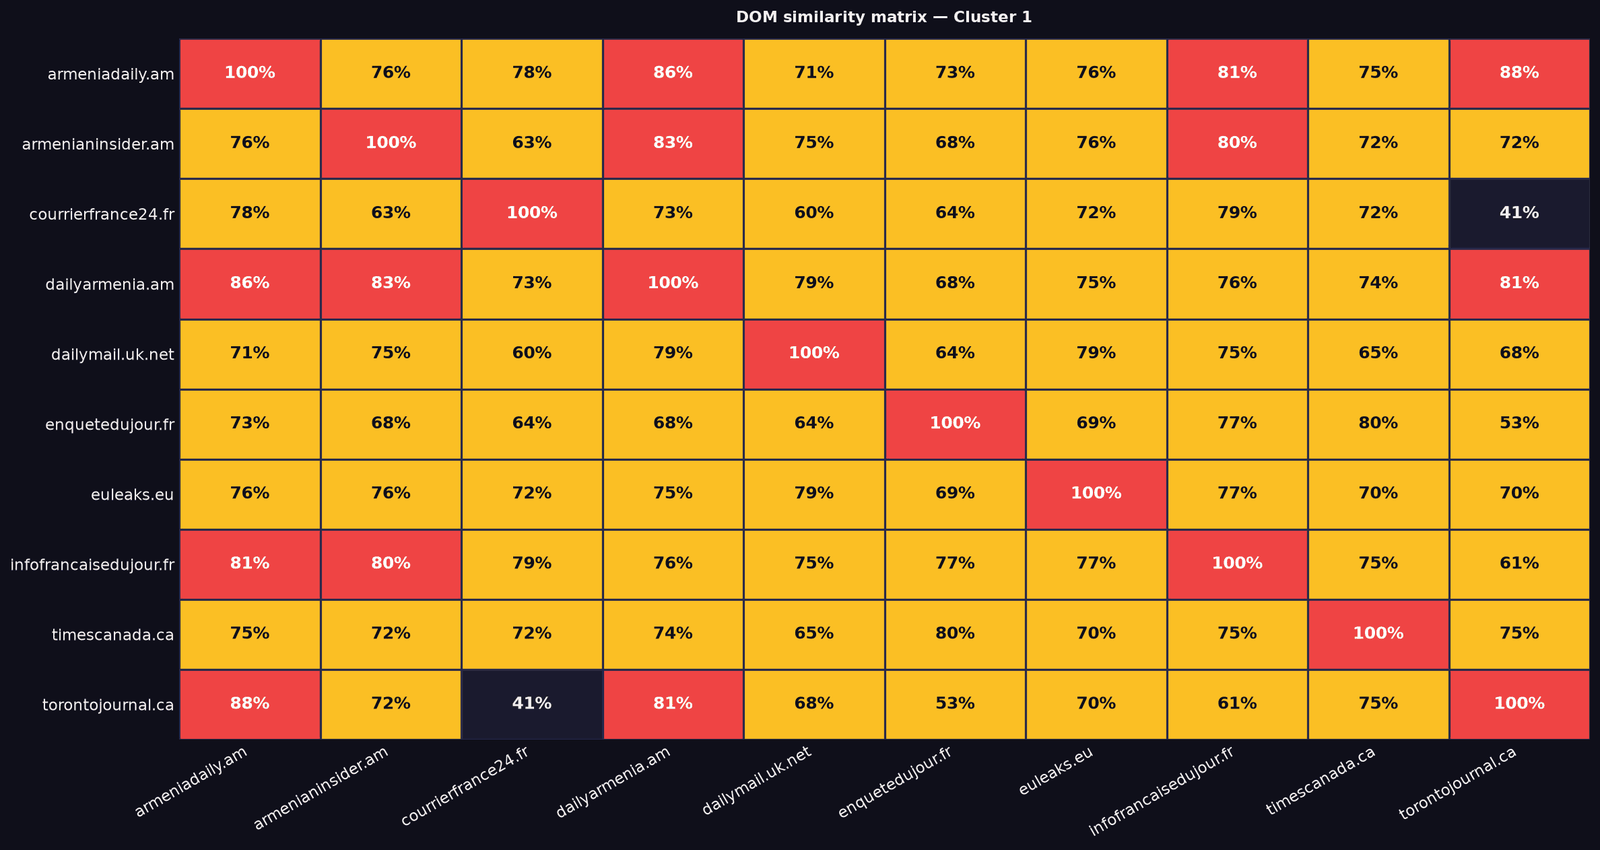
Up to 98.5% identical page structure between outlets claiming no relation to each other.
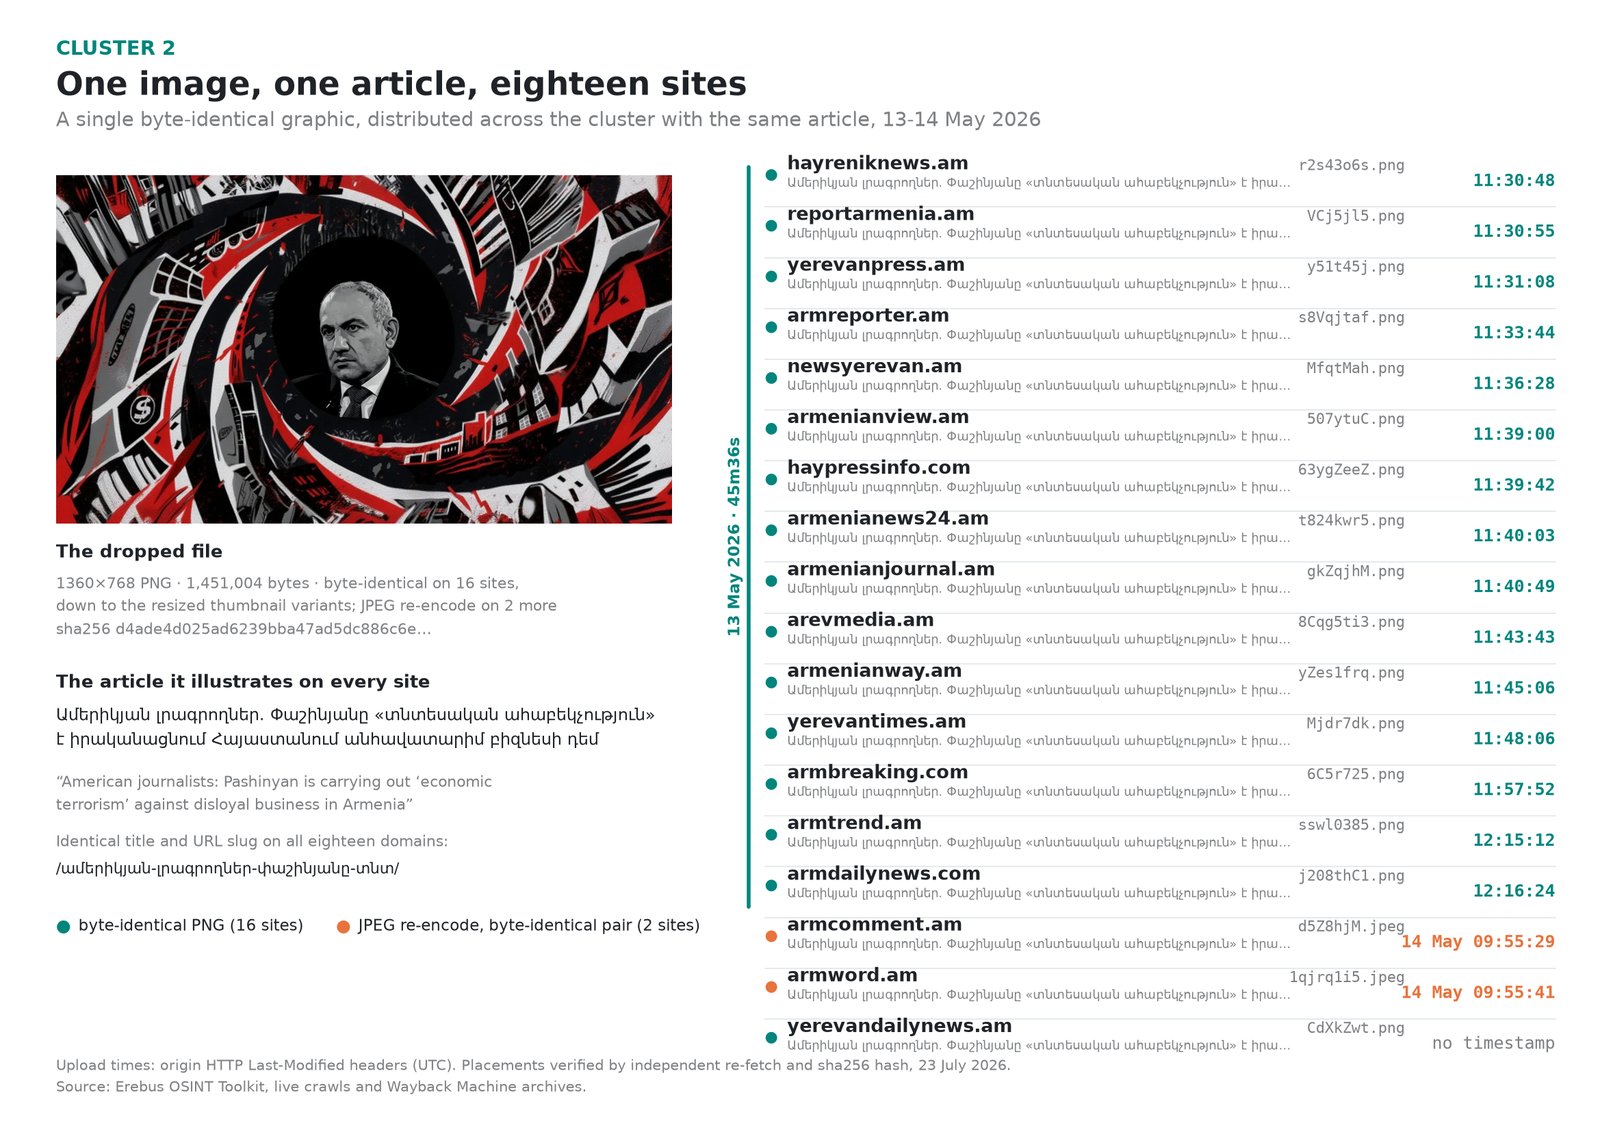
476 byte-identical images recurring across an 18-site amplifier fleet.
A filename fingerprint binding all eighteen sites of the amplifier cluster to shared tooling.
45 campaigns of fabricated stories, from invented assassination plots to manufactured scandals, attributed to the operation.
For a year before Armenia voted on June 7, 2026, accounts on X posted short fake videos about the country, many dressed as reports by the BBC, Reuters or Euronews, into the replies of fact-checkers and newsrooms. With CivilNet we mapped the accounts and how they behaved, and assess the activity as likely part of the pro-Russian operation known as Matryoshka.
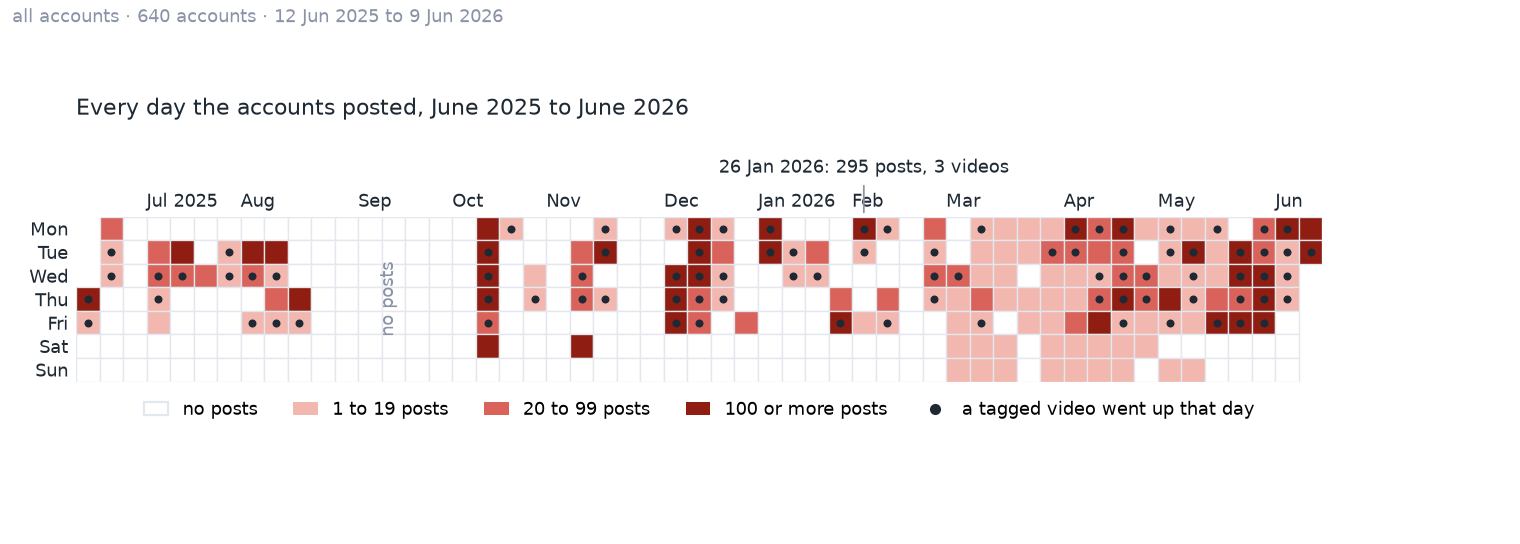
620 tagged posts carrying 287 fake videos from June 2025 to June 2026, posted by 593 of 640 listed accounts.
Not one of 612 dated posts went up on a Saturday or a Sunday, and the videos went out in batches, a median 8.6 minutes apart.
A median of one follower per account, against 9,450 for the legitimate Armenian newsrooms and journalists we compared them with.
One account, one video: 566 of the 640 accounts posted exactly one tagged video before a fresh batch took over.
7,745 replies under 2,269 accounts, most often fact-checkers, researchers and newsrooms: the videos were addressed to the people who check, not to voters.
Domain registration chains, hosting provider identification, shared infrastructure mapping across related domains, historical DNS records, and certificate transparency analysis.
Fingerprint Correlation
Matching infrastructure patterns against known threat actor tooling and techniques. Identifying when disinformation sites share technical signatures with previously attributed operations.
Social Network Forensics
Coordination detection across social platforms: networks of accounts amplifying the same operation, cross-platform behavioral fingerprints, and the link from social amplification back to website infrastructure.
Attribution Analysis
Connecting infrastructure findings to assess coordinated activity, identify operational patterns, and build the forensic evidence base for threat actor attribution.
STIX 2.1 Intelligence Production
All findings delivered as structured threat intelligence in STIX 2.1 format, directly compatible with MISP, OpenCTI, and standard CTI platform workflows.
Services
How we work with you
Forensic Analysis
We take suspected disinformation sites from your existing pipeline and deliver full infrastructure forensic reports with STIX 2.1 formatted intelligence products.
Findings Debrief
Structured presentation of forensic results to your analysts and stakeholders. What we found, what the infrastructure patterns reveal, and what it means for your threat picture.
Technical Workshop
Hands-on training in OSINT infrastructure forensics methodology. Your analysts learn to trace registration chains, identify hosting clusters, and produce actionable intelligence.
Threat Landscape Briefing
Assessment of disinformation infrastructure targeting your sector or region, based on our ongoing detection work and research findings.
Dataset Delivery
When you want the data rather than the analysis, we are the collection layer. You receive a dated bundle in the format you work in — CSV, NDJSON, SQLite or STIX 2.1 — with a data dictionary describing every column and a manifest carrying a SHA-256 for every file, row counts, the date window and the collector versions. Verifiable on arrival, not on trust.
Simulation
Watch a disinformation attack unfold
One minute inside our simulation engine: self-learning malicious agents attack a modeled population and learn how to maximize distrust. The same dynamics we hunt in the wild, and the environment we use to train analysts and stress-test defenses.
Erebus simulation engine / adversarial influence campaign against a population model
Background
Why us
01
Published record. Our investigations attributing live influence operations are published, with the forensic evidence public and co-authored with established research institutions.
02
Documented methodology. OSINT methodology for identifying and technically fingerprinting disinformation infrastructure, developed through real-world detection and attribution work.
03
Standards-based output. Intelligence delivered in STIX 2.1 format, directly compatible with MISP, OpenCTI, and existing CTI workflows.
04
European threat landscape. Focused on hybrid threats and influence operations targeting European infrastructure and institutions.
Get in touch
Contact
We work with government agencies, defense organizations, election bodies, CTI teams, and platform integrity teams across Europe. If you are dealing with a coordinated network targeting your country, sector, or platform, we should talk.